Maileva: 22 million data theft at La Poste, investigation opened
Maileva, a subsidiary of La Poste, fell victim to a cyber attack in mid-September that exposed the data of 22 million people. A judicial investigation is under way following notification to the CNIL.
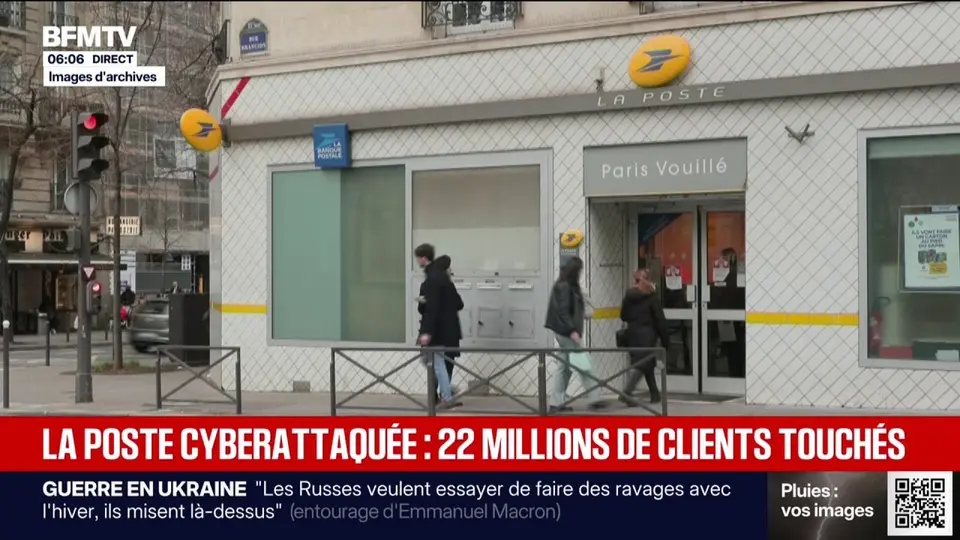
Massive breach at La Poste subsidiary Maileva
Maileva, a digital mail management platform run by La Poste, suffered a cyber attack in mid-September that resulted in the theft of personal data belonging to 22 million people, the group announced on Saturday 14 November. According to BFM TV and specialist website cyberattaque.org, it is one of the most significant data breaches recorded in France.
The stolen data includes names, surnames and postal addresses of recipients of Maileva's services. Several thousand business clients of the group are affected, notably in the sectors of social housing, health and public services.
Maileva provides digital mail sending services to small and medium-sized enterprises as well as mid-sized enterprises, processing administrative documents such as payslips, registered mail, invoices and general assembly notices. The platform claims more than 70,000 users, with 180 million documents sent in 2024. It is a subsidiary of Docaposte, itself a subsidiary of La Poste.
Maileva notified the National Commission for Computing and Liberties (CNIL) and filed a complaint with the authorities, according to statements from La Poste. A judicial investigation is under way to determine the origin and scale of the breach.
La Poste stated that "in accordance with regulations", all affected companies were informed of the incident by Maileva. This notification follows the legal obligations under the General Data Protection Regulation (GDPR), which requires rapid disclosure in the event of a personal data breach.
This cyber attack illustrates the growing risks faced by digital service providers managing vast volumes of sensitive data. Maileva processes confidential information daily for companies operating in critical sectors, making its infrastructure an attractive target for malicious actors. The absence of public details on the method used for the breach – nor any claim of responsibility by any group – currently limits analysis of the exact circumstances of the security flaw.
Professional clients of Maileva will need to assess the potential impact on their recipient records and strengthen their security protocols for subsequent communications. Individuals whose contact details have been exposed should remain vigilant against potential identity theft or postal fraud attempts using this information.
The CNIL is the French authority responsible for investigating personal data breaches and can impose administrative penalties on those responsible for processing. The results of its examination and the judicial investigation will determine whether fines will be imposed on La Poste and what corrective measures will be ordered to prevent future incidents.
Source: BFM TV