Worten cyber attack: expert warns of risk of unauthorised direct debits
Cybersecurity expert criticises "negligent" approach by Worten after cyber attack that exposed customers' IBANs. Recommends urgent verification with banks.
IBAN data exposed in Worten attack raises cybersecurity expert's concerns
The cyber attack on Worten, disclosed on Wednesday, represents a threat that affected customers should not underestimate, according to cybersecurity expert Nuno Mateus-Coelho, cited by CNN Portugal. The expert describes the situation as "a complicated matter", arguing that "an important part of the data the company lost included people's IBANs".
Mateus-Coelho regrets that Worten did not issue "a clear warning" to customers: in his opinion, all should have received a recommendation to check, in the following weeks, whether any direct debit had been created without authorisation. The expert emphasises that this alert is "relevant" because there is a 13-month period to claim reimbursement from the bank for unauthorised transactions.
Risk of "highly credible" social engineering
The danger does not end with direct debits. With the data obtained, attackers are in a position to orchestrate "very, very credible social engineering campaigns", Mateus-Coelho warns. "They'll get the customer's name right, they'll get the address right, they know about order A, B or C, and they'll say a series of things so credible that it will make people click", added the also university professor. The conclusion is straightforward: "They have everything."
The expert classifies as "negligent" Worten's decision not to direct customers to verify with their respective banking institutions whether new unauthorised debits had appeared. "It was they who lost the data", he recalls.
The advice he gives to customers is equally direct: distrust any communication that appears to come from Worten or entities in its sphere, and always confirm its authenticity through an independent channel.
What Worten said about the compromised data
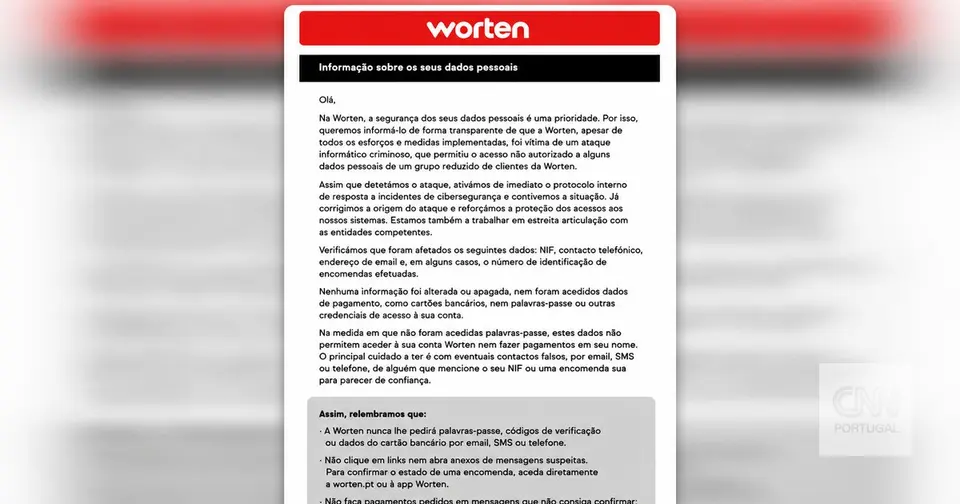
In the email sent to affected customers, Worten acknowledged that the attack "allowed unauthorised access to some personal data of a small group of customers". The company listed as compromised data the NIF (taxpayer identification number), telephone contact, email address and, in some cases, the order identification number — without making any reference to IBAN numbers.
"The main thing to be careful about is any false contacts, by email, SMS or telephone, from someone who mentions your name or your order to appear trustworthy", the company warned in the same email.
In a statement sent to Lusa news agency, Worten described the incident as "a criminal act of unauthorised access to some customer and service provider data". The company guaranteed that "no information was altered or deleted, no credit or financial data or access credentials were accessed, and the normal functioning of systems was not affected", based on a forensic investigation still in progress.
Measures adopted and coordination with authorities
Worten stated it had corrected the vulnerability that was exploited and strengthened access controls. The company also indicated it is "in full coordination" with the National Cybersecurity Centre, the National Data Protection Commission and the Judicial Police.
The retailer guaranteed that it has already "directly informed all affected customers" and that it is also notifying the targeted service providers. "At Worten the priority is the security of personal data and systems under our responsibility, whether such data concerns customers, employees or suppliers", states the released statement.
Source: CNN Portugal