Tens of thousands of UK fridges secured from hackers in secret operation
A covert cyber-security operation has protected tens of thousands of UK fridges and freezers from hackers. Supermarkets, warehouses and stadiums were among those targeted.
Secret UK operation secures tens of thousands of fridges from cyber-attack
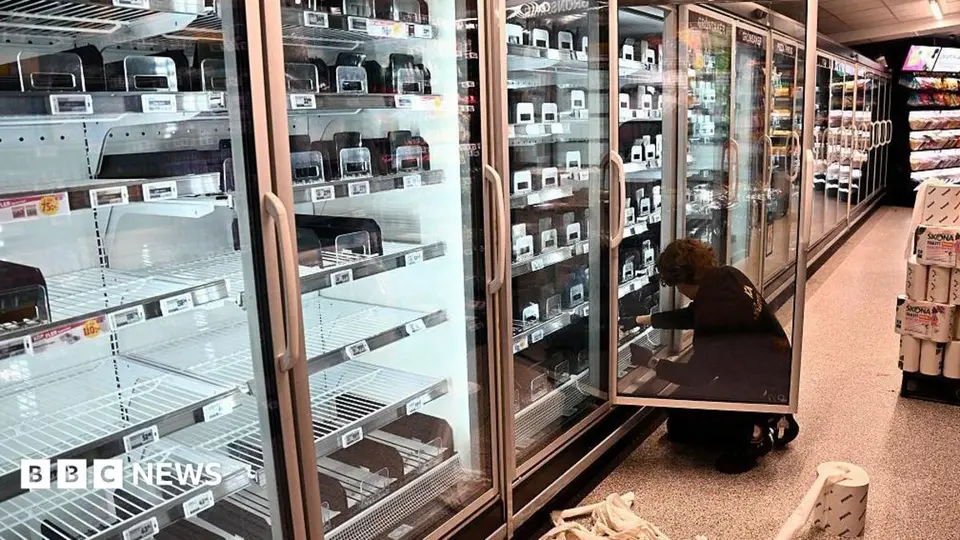
A covert cyber-security operation has been carried out to protect tens of thousands of refrigeration units at major UK supermarkets, warehouses, restaurants, petrol stations and stadiums from hackers, BBC News has learned.
The operation came in response to a series of cyber-attacks across Europe this year that spoiled tonnes of food at hundreds of stores, causing millions of pounds in damage. France has blamed Iran for one wave of attacks that struck its supermarkets — a claim Tehran denies.
Vulnerability discovered in late October
It had been widely assumed that the UK was largely insulated from such attacks because the British refrigeration industry relies on different equipment from that targeted on the continent. In late October, however, security researchers discovered a significant flaw in devices widely used across the UK that, if exploited, could have caused even greater disruption.
Since that discovery, researchers, IT teams and the National Cyber Security Centre (NCSC) have been working around the clock to alert dozens of companies. BBC News held back reporting on the operation until now in order to reduce the risk of hackers acting on the vulnerability before it could be fixed.
The flaw was first identified by ethical hackers at a firm called Omega Systems. Experts at Pentest Partners then verified and extended the findings and helped raise the alarm. The NCSC, the Department for Environment, Food & Rural Affairs (Defra) and the Food Standards Agency (FSA) all became involved in the subsequent effort to close the security gaps, holding industry conference calls and tasking teams with contacting companies at risk.
Devices taken offline across the country
Thousands of controllers — each capable of managing the temperature of dozens of fridges and freezers — were taken off the open internet, either remotely or, in some cases, physically. Staff at affected sites were instructed to remove internet cables and monitor temperatures by hand.
BBC News has learned that most major supermarkets were forced to divert IT teams to address the risks. A worker at one large chain said they took hundreds of devices offline every day over the course of a week.
"It did feel like a race against time as we were expecting another wave of these fridge hacks to come," the person said, declining to be named publicly. "From a business perspective it could have been potentially devastating with business interruption and supply chain problems. Our warehouses have millions of pounds worth of food that could have been spoiled if any hackers found out about this method of attack."
Three waves of attacks already this year
There have been three separate waves of attacks on refrigeration temperature controllers in 2024:
- August: Fridges at a small number of US military bases were affected.
- 11–12 October: Hundreds of supermarkets and food processing sites in France were hit when Danfoss temperature control systems were targeted.
- 1–2 November: Dozens of supermarkets across seven European countries were struck, with Belgium and Luxembourg the worst affected. A small number of blood bank sites in France were also impacted.
Those attacks prompted an expert at Omega Systems to examine the security of the UK's most widely used refrigeration controllers, manufactured by British firm Resource Data Management (RDM).
RDM disputes severity but praised for response
Ken Munro of Pen Test Partners said the RDM controllers shared a vulnerability with those attacked successfully in Europe. "These popular controllers had a similar weak password problem to the Danfoss and other controllers that were attacked so successfully in previous hacks, so we had to get the message out as soon as possible and keep it secret," he said. "There is so much extra attention on these ubiquitous bits of kit now that it was likely a matter of days until criminals or nation state hackers figured it out."
RDM disputes that the comparison with European units is a fair one, arguing that hacking its fridges and freezers would have required access to a piece of hardware. The ethical hackers counter that this would have been achievable, since the hardware can be purchased cheaply online through sites such as eBay.
Ged Evans, CEO of RDM, said the test environment used by the researchers "went beyond" what such exercises normally involved, as it "included dismantling our hardware." He added that the company had "acted at pace" to address the issue, deploying its first patch releases and contacting customers proactively to recommend mitigating steps.
RDM confirmed there is no sign of any malicious activity on its controllers and that it continues to work with the NCSC and other authorities to monitor the situation. Despite disputing the critical nature of the vulnerabilities identified, RDM has been praised for its professional response, BBC News understands.
Wider food and beverage industry warned
Beyond supermarkets, a broad range of sectors within the UK food and beverage industry were also warned to take action, including convenience stores, petrol stations, restaurants and fast food chains, sports arenas, hotels, food processing plants and cold storage sites.
Source: BBC News